Data Protection Risks and How to Mitigate Them in Australia
How much data does your business have sitting on its systems right now?
Think about customer details. Employee records. Emails. Financial information. Old files on laptops. Data stored in cloud accounts.
Now think about what would happen if someone accessed that information without permission.
For many Australian businesses, data protection is no longer something that can sit with the IT team alone. Business owners and managers also need to know where their data goes and how it is protected.
A security incident can affect more than your systems. It can interrupt daily operations and create privacy problems. It can also affect the trust people have in your business.
So, what are the main data protection risks for Australian businesses?
Let’s take a closer look.
In short
Businesses can face data protection risks at many points.
The problem might start with a phishing email. It could also come from an old user account or a poorly protected cloud system.
Even an old computer sitting in a storage room can become a risk if it still contains sensitive information.
The most common risks include:
- Cyberattacks
- Unauthorised access
- Human error
- Poor data retention
- Third-party access
- Insecure IT asset disposal
- Privacy compliance gaps
- Slow data breach response
The good news is that most of these risks can be reduced with the right processes.
Why Does Data Protection Matter for Australian Businesses?
Businesses collect data because they need it to operate.
A customer may give you their contact details. An employee may provide personal information during onboarding. A client may share sensitive documents with your team.
The problem starts when businesses lose track of that information.
You may know where your main database is. But what about an employee’s laptop? What about an old server? What about a former employee’s account?
Data protection is about looking at the whole picture.
The OAIC says organisations covered by the Privacy Act need to take reasonable steps to protect personal information. This includes protection against loss and unauthorised access or disclosure. (OAIC)
Data Protection Risk #1: Cyberattacks
A business does not have to be a large corporation to attract cybercriminals.
A phishing email can reach a small business just as easily as it can reach a large company.
An employee might click a fake login link. An attacker could then use those credentials to access business systems.
Ransomware is another concern.
It can lock access to important files and bring normal business activities to a stop.
How can you reduce the risk?
Start with the basics.
Make sure important accounts use multi-factor authentication. Keep software and operating systems updated. Review administrator access and remove permissions that are no longer needed.
Backups also matter.
Your backup should not simply exist. You need to know that it can actually be restored when you need it.
The Australian Signals Directorate recommends the Essential Eight as a baseline for reducing cyber security incidents. The framework includes patching, multi-factor authentication, restricting admin privileges and regular backups.
💡 Tips for your business
Use MFA on important accounts.
Update software regularly.
Limit admin access.
Train your staff about phishing.
Test your backups.
Data Protection Risk #2: Unauthorised Access
Sometimes the problem is not a hacker breaking through your security.
It can be someone who already has access.
Consider how many people in your business can access customer information.
Does everyone really need the same level of access?
Probably not.
An employee in accounts may need access to billing information. They may not need access to every customer record in your system.
Keeping access limited makes it harder for information to be exposed.
It also means there is less damage if an account is compromised.
What should businesses check?
Review user accounts regularly.
Look for old accounts that are still active. Check access when employees change roles.
Most importantly, make sure former employees no longer have access after they leave.
This sounds simple.
Yet old accounts can easily be missed when businesses grow or staff changes happen quickly.
Data Protection Risk #3: Human Error
Technology is only part of the problem.
People can make mistakes too.
An email can be sent to the wrong person. A confidential file can be uploaded to the wrong folder. A laptop can be left behind at an airport or on public transport.
These situations can happen even when a business has good security systems.
That is why employees need to understand their role in data protection.
How can businesses reduce human error?
Training does not need to be complicated.
Show employees how to spot suspicious emails. Explain what information should not be shared. Make sure they know who to contact if something goes wrong.
It is also important to make reporting easy.
An employee who realises they have made a mistake should feel comfortable reporting it straight away.
The faster a business knows about a problem, the faster it can act.
Data Protection Risk #4: Keeping Data You No Longer Need
Here is a question worth asking:
Why are you still keeping that data?
Many businesses have old records sitting in databases and backup systems.
Some of that information may no longer serve a business purpose.
The longer you keep personal information, the longer you are responsible for protecting it.
The OAIC says covered organisations need to take reasonable steps to destroy or de-identify personal information when they no longer need it for a permitted purpose. There are exceptions where another law or a court order requires the information to be retained.
This makes data retention worth reviewing.
What should you look at?
Start with your older data.
Look at customer records. Check old employee information. Review data stored in legacy systems.
Ask why it is still there.
If you no longer need it, check whether it can be securely destroyed or de-identified.
This can reduce the amount of information your business needs to protect.
Data Protection Risk #5: Your Old IT Equipment
This is an area that businesses sometimes forget.
A computer can be old without the data on it being old.
An employee may have stored customer details on a laptop for years. A server may contain information from multiple business systems.
Now imagine that equipment is sent away for recycling without proper data sanitisation.
The hardware may no longer be useful to your business. The information on it may still matter.
How should businesses handle old equipment?
Have a process for retired IT assets.
Track what equipment is leaving the business. Check what data may be stored on it.
Then use an appropriate method to securely erase or destroy the data.
The OAIC recognises methods such as hardware sanitisation and physical destruction. It also says businesses should take reasonable steps to verify and document destruction or de-identification where required.
This is why secure IT asset disposal should be considered part of your data protection process.
Data Protection Risk #6: Third-Party Providers
How much of your data is actually managed by your own business?
You may use cloud software. You may work with an IT provider. You may use external storage or other technology services.
That means your data may be handled outside your direct control.
This does not mean you should avoid third-party services.
It means you should understand how those services handle your information.
Before signing a contract, ask some straightforward questions.
Where is the data stored?
Who can access it?
How is it protected?
What happens when the contract ends?
What happens to your information if the provider has a data breach?
Cross-border arrangements also deserve attention. APP 8 sets requirements around certain overseas disclosures of personal information.
Data Protection Risk #7: Privacy Compliance Problems
Data protection is not only an IT issue.
Australian businesses also need to understand the privacy obligations that apply to them.
The Privacy Act does not cover every business in exactly the same way.
For example, most small businesses with an annual turnover of $3 million or less are generally exempt. There are important exceptions though. These include certain health service providers and businesses that trade in personal information.
So, do not assume that your business is exempt simply because it is small.
The rules can depend on what your business does and what information it handles.
Where should a business start?
Start with a simple data review.
Find out what personal information you collect.
Then look at how it is used and where it is stored.
Check who has access to it.
A privacy impact assessment can also help when introducing a new system or project that involves personal information. The OAIC recommends using privacy impact assessments as part of planning and risk management.
What Happens When a Data Breach Occurs?
No business wants to deal with a data breach.
But having a plan before something happens can make the situation much easier to manage.
Imagine discovering that an employee account has been compromised.
Who investigates it?
Who decides whether customers need to be contacted?
Who handles communication with the OAIC?
Who isolates the affected systems?
These are much easier questions to answer when you already have a response plan.
Under Australia’s Notifiable Data Breaches scheme, certain data breaches must be reported when they meet the requirements for an eligible data breach. Serious harm is an important part of that assessment.
For businesses covered by the scheme, suspected breaches should be assessed promptly. The OAIC expects the assessment to be completed within 30 calendar days at the latest after becoming aware of the circumstances that may amount to a breach.
The key point is simple.
Do not wait until a breach happens to decide what your response should look like.
How Can Australian Businesses Reduce Data Protection Risks?
You do not need to fix everything in one day.
Start by understanding your current position.
Where is your data?
Who can access it?
Which systems hold it?
What happens when an employee leaves?
What happens when an old computer is removed?
Once you know where the gaps are, you can start addressing them.
💡 A practical starting point
Review important user accounts.
Turn on MFA.
Update old software.
Check your backups.
Review third-party access.
Create a data retention process.
Secure old IT equipment before disposal.
Keep your privacy policy up to date.
Create a data breach response plan.
These steps can give your business a much clearer view of its data protection position.
Does Data Protection End When an Employee Leaves?
It should not.
Employee departures can create a number of data protection issues.
Think about company laptops. Think about email accounts. Think about access to shared drives and cloud systems.
A departing employee may have access to business information right up until their account is disabled.
At the same time, the device they return may contain business and personal information.
A proper offboarding process should cover both access and equipment.
Accounts should be reviewed and disabled.
Returned devices should be handled through your normal IT asset disposal or redeployment process.
What About Data on Old Hard Drives?
This is worth taking seriously.
A hard drive can contain much more than the files a user can see.
Deleting a file does not automatically mean the information has been securely destroyed.
The right approach depends on the type of storage device and the sensitivity of the information.
For some assets, secure sanitisation may be suitable. For others, physical destruction may be appropriate.
The important thing is to use a method that matches the risk.
The OAIC notes that electronic information can require hardware sanitisation or another method of irretrievable destruction.
A Simple Data Protection Check for Your Business
Take a few minutes and ask yourself these questions.
Do we know where our sensitive data is stored?
Do we know who can access it?
Do we still need all the data we keep?
Are old employee accounts removed?
Are our important systems protected with MFA?
Are our backups tested?
Do we know how our suppliers handle business data?
What happens to data on retired computers?
Could our team respond quickly to a data breach?
If several answers are unclear, it may be time to review your current processes.
Data Protection Risks: Conclusion
Data protection can feel like a big job.
It does not have to start that way.
Look at what your business already does.
Check how information enters the business. Look at where it is stored. Review who can access it.
Then think about what happens when that information is no longer needed.
That last part is easy to overlook.
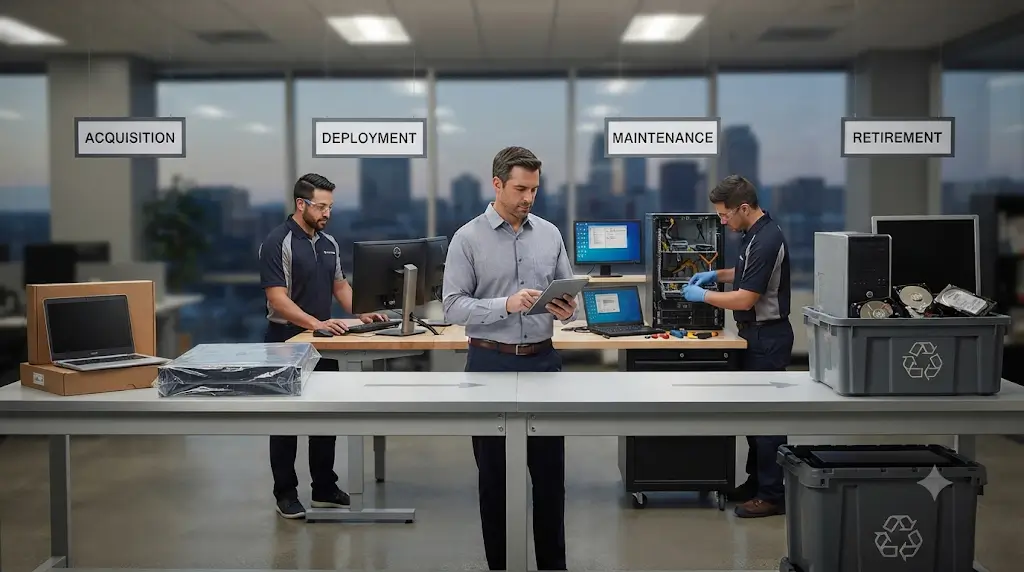
Old computers and storage devices can continue to hold sensitive information long after they have left active use. Secure data destruction should therefore be part of the wider IT asset lifecycle.
For Australian businesses, good data protection comes down to having the right controls in place and reviewing them regularly.
It is not only about protecting data today.
It is also about making sure that data remains protected when systems change and when IT equipment reaches the end of its life.
Cyber Recycling helps Australian businesses manage retired IT equipment through secure data destruction services and responsible IT asset disposal. This can help businesses take care of the final stage of their IT asset lifecycle while reducing the risk of data remaining on unwanted equipment.
Note: Privacy obligations vary between businesses and industries. This article provides general information and should not be treated as legal advice.
 Copy Link
Other Blog
The 5 Stages of IT Asset Lifecycle…
11-19-2026
IT asset lifecycle management controls every IT asset from the moment a need is identified through to secure…
Why Your Business Needs an E-Waste Management…
11-19-2026
An e-waste management strategy is a documented plan for how an organisation stores, sanitises, reuses and recycles retired…
Lithium-Ion Battery Fire Hazards in the Workplace:…
11-17-2026
Lithium-ion battery fire hazards are highest when equipment is retired and placed in storage. Laptops, phones, power tools…